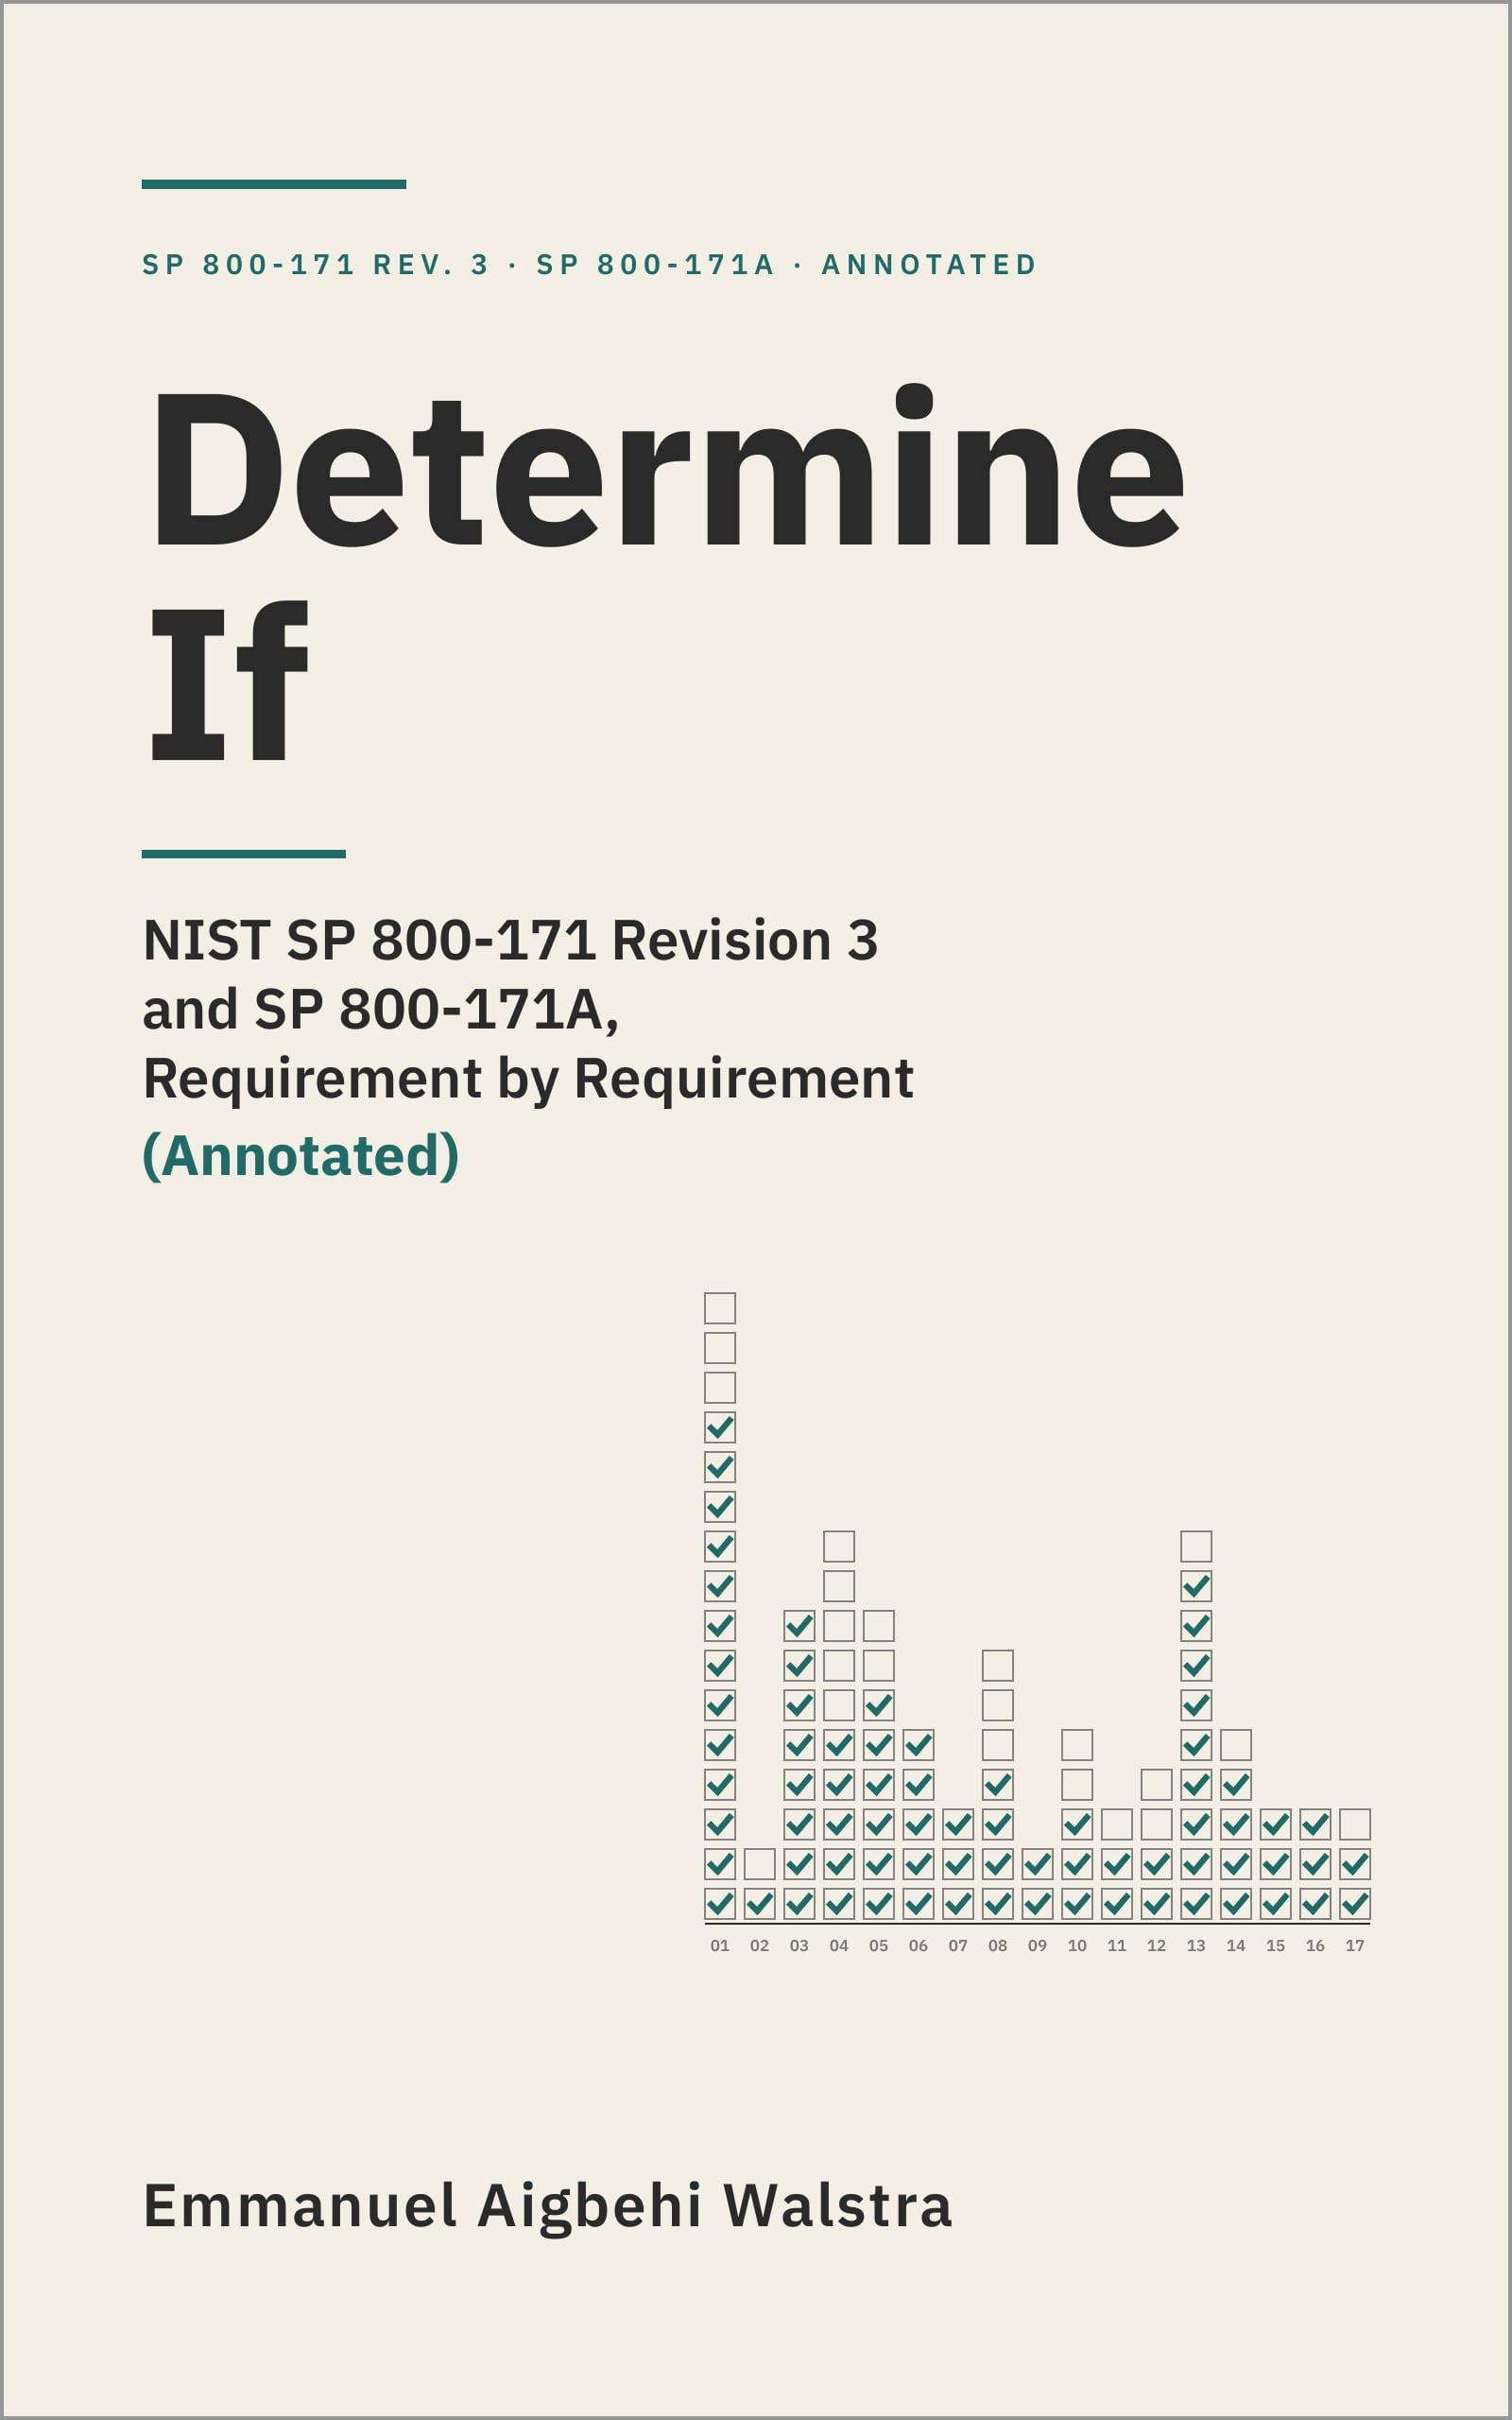
Determine If
NIST SP 800-171 Revision 3 and SP 800-171A, Requirement by Requirement (Annotated)
Hardcover ($44.99): Hardcover coming soon (not on Amazon yet; KDP submissions start after 1 Nov 2026)
What this edition adds to the free NIST publication
SP 800-171 and SP 800-171A are public domain and free to download from NIST. You pay for the annotation, evidence and mapping work in this edition, not for the NIST text.
| NIST SP 800-171 Rev. 3 and SP 800-171A Rev. 3 (free) | This annotated edition | |
|---|---|---|
| Requirements and assessment procedures | Two separate publications | Each requirement printed with its Discussion, every "Determine if" statement and the assessment methods, in one unit |
| Changes from Rev. 2 | A separate change analysis workbook | NIST's change summary on every requirement, plus a crosswalk covering all 110 Rev. 2 requirements |
| What each requirement means in practice | Not in these publications | Practice notes for all 97 requirements |
| Evidence | Generic lists of potential assessment objects | 364 specific evidence items, three to five per requirement |
| Common findings | Not in these publications | 291 illustrative findings, three per requirement |
| Maturity | Not in these publications | A four-step maturity strip for each requirement |
| Mappings | SP 800-53 source controls | Rev. 2 lineage, SP 800-53 source controls, CMMC Level 2 identifiers and ISO/IEC 27001:2022 Annex A numbers on every requirement |
| Organization-defined parameters | Listed requirement by requirement | An 88-entry register with a blank column for your values, plus 24 implementation worksheets |
What the annotation work gives you:
- 97 requirement units. Each puts the SP 800-171 requirement, its Discussion and its full SP 800-171A assessment objective together, so you never have to switch between two documents.
- 97 commentary pages, one per requirement, with practice notes written for the people who implement and assess the requirement.
- 364 evidence items, three to five per requirement: what assessors look for.
- 291 common findings, three per requirement and labelled illustrative, which you can use as a pre-assessment checklist.
- 97 four-step maturity strips: Initial, Defined, Implemented, Managed.
- A mapping panel on every requirement: Rev. 2 lineage and SP 800-53 Rev. 5 source controls (NIST), CMMC Level 2 practice identifiers and ISO/IEC 27001:2022 Annex A numbers (derived; numbers only).
- 24 implementation worksheets with fields for your ODP values, a Met / Not met / N/A result for each determination statement, owner, review dates and POA&M reference. They follow the requirements whose NIST text runs to two pages.
- An 88-entry ODP register with a blank column for your chosen values, ready for your System Security Plan.
- 17 family openers with a diagram of each family's active, new and withdrawn requirements, a Rev. 2 to Rev. 3 crosswalk of all 110 Rev. 2 requirements, the SP 800-172 Rev. 3 enhanced requirement statements, and the status of CMMC and the proposed FAR CUI clause as of October 2026.
Look inside


Description
Every SP 800-171A assessment objective begins with the same two words: determine if. This annotated edition sets out all 97 active security requirements of NIST SP 800-171 Revision 3 so you can see what each requirement says, what an assessor will determine, and what evidence answers it. NIST text is re-typeset with the wording unchanged and labelled NIST VERBATIM.
The requirements and discussion from SP 800-171 Rev. 3, the assessment objectives and methods from SP 800-171A Rev. 3, NIST's Rev. 2 to Rev. 3 change analysis, and the SP 800-172 Rev. 3 enhanced requirements, re-typeset with the wording unchanged.
What's inside
- Before you start (pp. 7–15): How to use this book; Mapping method and caveats; Where things stand: October 2026; How to read an SP 800-171A procedure; About the author
- Part I — NIST's Introduction (p. 17): Introduction and The Fundamentals (SP 800-171r3); The Fundamentals (SP 800-171Ar3)
- Part II — The Requirements, Annotated (p. 27): all 17 families, 03.01 Access Control through 03.17 Supply Chain Risk Management, one unit per active requirement
- Part III — Beyond the Baseline (p. 307): SP 800-172 Rev. 3 enhanced security requirements
- Appendices (p. 323): A Revision 2 to Revision 3 crosswalk; B Organization-defined parameter register; C Glossary (SP 800-171r3); D References (SP 800-171r3); E Sources for this edition; Index
Who it is for
Security managers, compliance leads, assessors and consultants in the defense industrial base and other organisations that handle Controlled Unclassified Information. The status of CMMC and the proposed FAR CUI clause is given as of October 2026, with sources.
About the author
Emmanuel Aigbehi Walstra is a CISO who also serves as a virtual CISO (vCISO) for several organisations, with 30+ years in cybersecurity, 10,000+ people trained, and author of the CCSP Excellence books.
Independent companion
This book is an independent companion to the NIST publications. It is not affiliated with or endorsed by NIST, the U.S. Department of Commerce, the U.S. Department of War, the Cyber AB or ISO/IEC. Mappings between frameworks are reading aids, not official equivalences. This book gives general information and is not legal, assessment or compliance advice.
Buy
- PDF edition (350 pages): https://sectutor.gumroad.com/l/determine-if — $24
- Hardcover ($44.99): Hardcover coming soon (not on Amazon yet; KDP submissions start after 1 Nov 2026)
Sectutor NIST Annotated Collection (all five), $79. All five Sectutor annotated NIST editions: CSF 2.0 (Outcomes to Evidence), AI RMF (Trust to Evidence), SP 800-171 Rev. 3 (Determine If) and SP 800-53 Rev. 5 Vol 1 and Vol 2 (Controls to Evidence).
PDF edition
$24